Originally reported by Deep Tide TechFlow on November 12, 2026, at 09:58 (UTC+8), translating a report jointly published by the Bitcoin Security Consortium and Presidio Bitcoin.
Quantum-computing advances have revived a familiar Bitcoin security question: could a future machine derive private keys from public keys? The report’s answer is not with any publicly demonstrated machine today. It argues that the gap between current hardware and a cryptographically relevant quantum computer remains large, while preparations for that possibility warrant attention.
What the risk actually covers
The report identifies two potential attacks on Bitcoin’s signature system, not on its issuance schedule, supply cap or consensus rules:
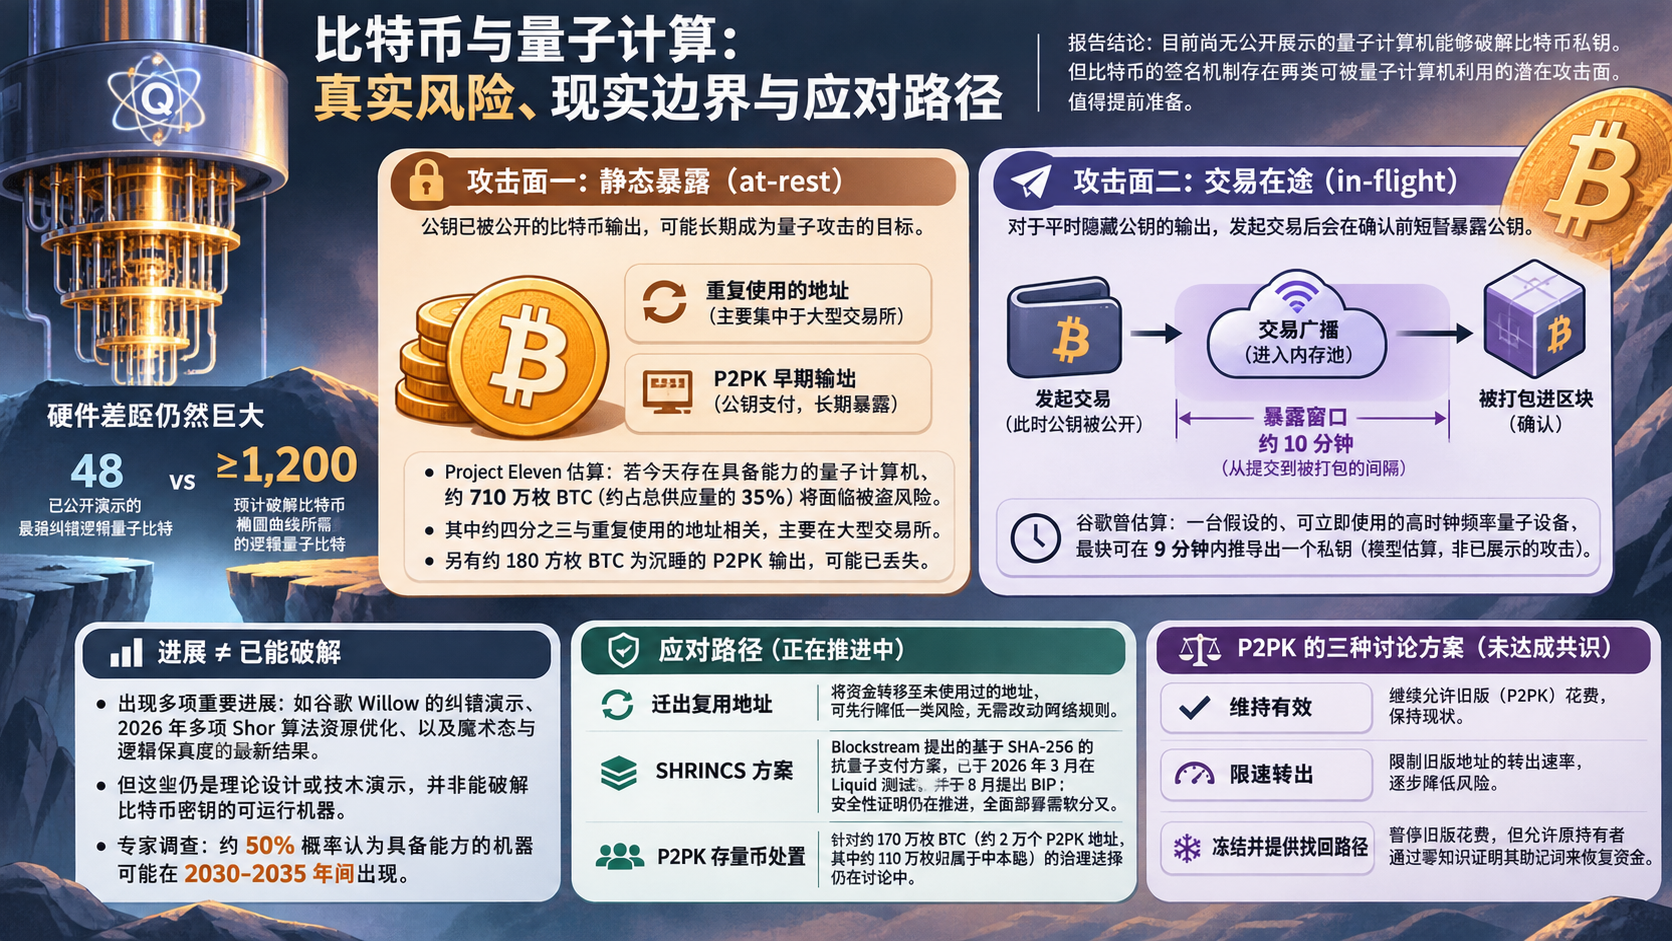
- Exposed keys at rest. Public keys are already visible for some coins, including those held at reused addresses and early pay-to-public-key (P2PK) outputs. Project Eleven estimates that, if a capable quantum computer existed today, roughly 7.1 million BTC, or about 35% of total supply, would be exposed to theft. The report says roughly three-quarters of that amount is associated with reused addresses, largely at major exchanges. It separately describes about 1.8 million BTC in dormant P2PK outputs as likely lost.
- Keys exposed during a transaction. For outputs whose public keys remain hidden until spending, broadcasting a transaction reveals the key before confirmation. The report describes this as a window of roughly ten minutes, though the actual interval runs from submission to inclusion in a block. It cites a Google estimate that a hypothetical, ready-to-use high-clock-speed quantum device could derive one private key in as little as nine minutes. That is a modeled risk, not a demonstrated attack.
The distinction matters: the report does not claim that all Bitcoin could be stolen at once. A key would have to be targeted individually, and many outputs do not expose a public key while unspent.
Progress is not a working attack
The report points to Google’s Willow error-correction demonstration, 2026 proposals to reduce the resources needed for Shor’s algorithm, and later results involving magic states and logical-qubit fidelity. It characterizes the Shor work as theoretical designs, not operational machines breaking Bitcoin keys. Its hardware comparison is stark: it says the strongest publicly demonstrated system had 48 error-corrected logical qubits, versus an estimated at least 1,200 needed to break Bitcoin’s elliptic-curve cryptography. Scaling reliable operations across that gap remains an engineering obstacle.
Nor does the report treat a breakthrough as safely decades away. It cites an expert survey assigning roughly a 50% probability to a capable machine emerging between 2030 and 2035, while cautioning that institutional post-quantum deadlines often address a different problem: encrypted private data captured now for decryption later. Those deadlines are not a forecast of a Bitcoin theft date.
The proposed responses—and the unresolved choice
Moving funds away from reused addresses to unused ones would reduce one category of exposure without a network rule change, the report says. It also describes Blockstream’s SHRINCS as a proposed SHA-256-based post-quantum payment scheme: Blockstream tested it on Liquid in March 2026, and a Bitcoin Improvement Proposal followed in August. The report says its formal security proof remained in progress and network-wide deployment would require a soft fork. It was not an enacted Bitcoin protection.
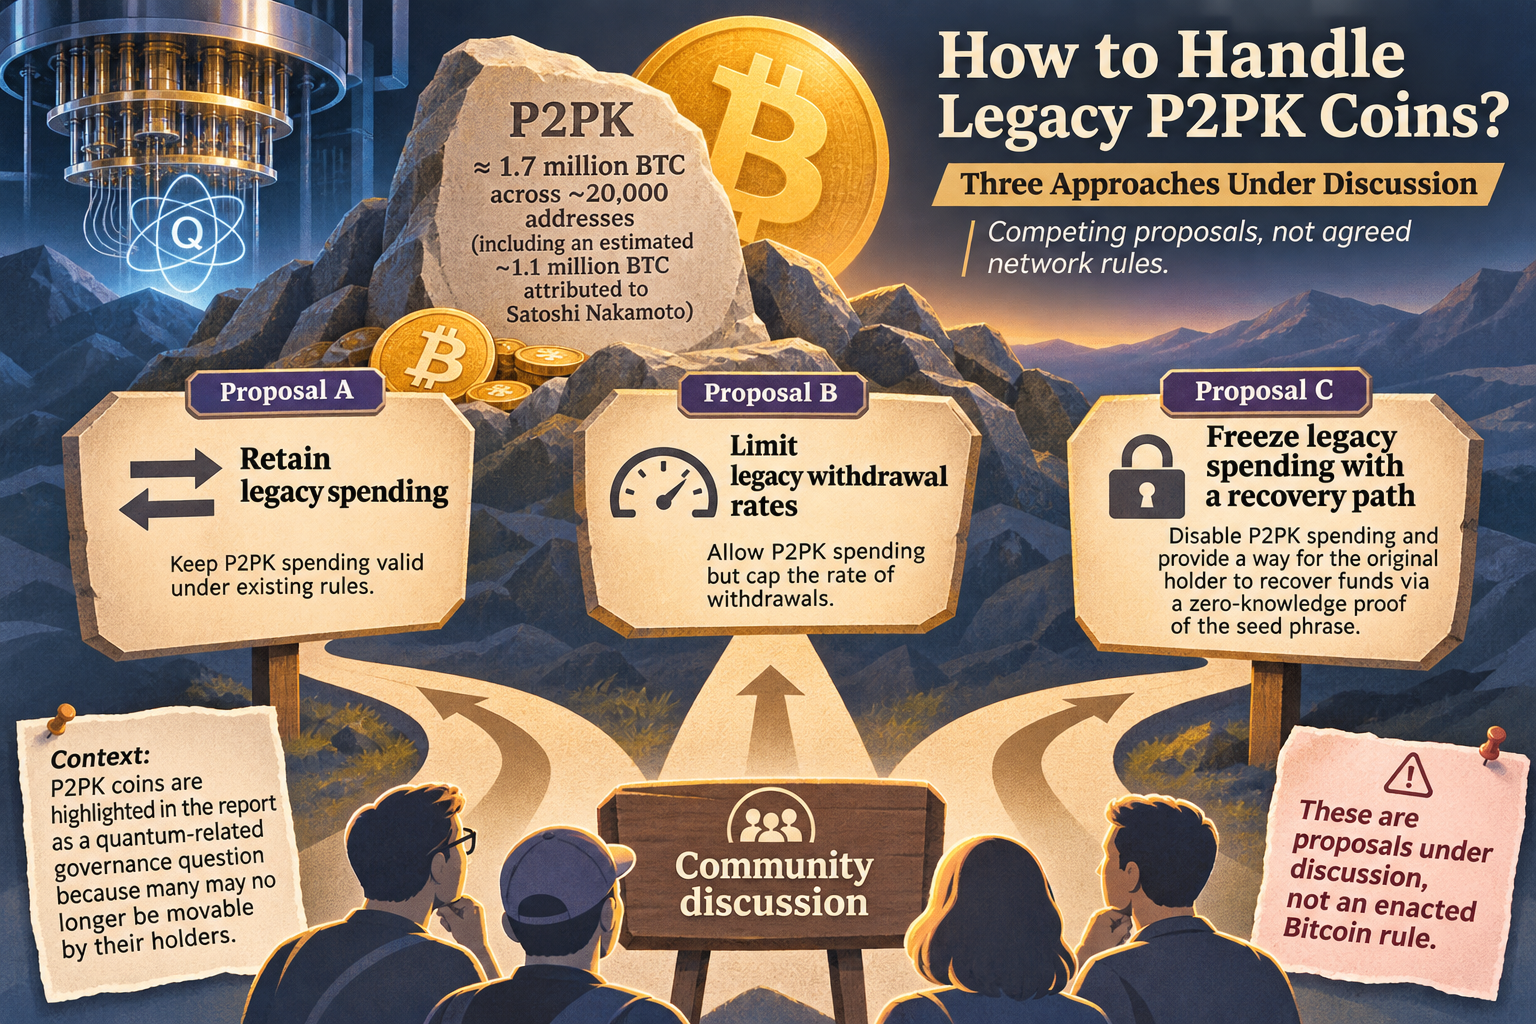
Older P2PK coins pose a harder governance question because their holders may no longer be able to move them. In a separate count, the report puts approximately 1.7 million BTC across 20,000 P2PK addresses, including an estimated 1.1 million BTC attributed to Satoshi Nakamoto. Presidio Bitcoin outlines three approaches under discussion: leave legacy spending valid, limit the rate of legacy withdrawals, or freeze such spending while providing a recovery path based on a zero-knowledge proof of the original holder’s seed phrase. These are competing proposals, not agreed network rules.
The quantum-risk narrative therefore rests on a real potential weakness in exposed public keys, but not on evidence that Bitcoin keys have been broken by a quantum computer. Its practical questions are which coins can be moved under existing rules, whether a proposed signature scheme can be validated and adopted, and what the network would decide about coins that may be lost.
Source: techflowpost.com (originally published 2026-11-12 09:58 UTC+8)